News · Issue 5
Inside the Wipe: How a Single Attacker Took Down Romania's Land Registry Database
Leaked passwords and unpatched bugs let one hacker freeze Romania's entire property market for a week. Here is how the break-in actually worked.
July 14, 2026
One agency, the whole property market
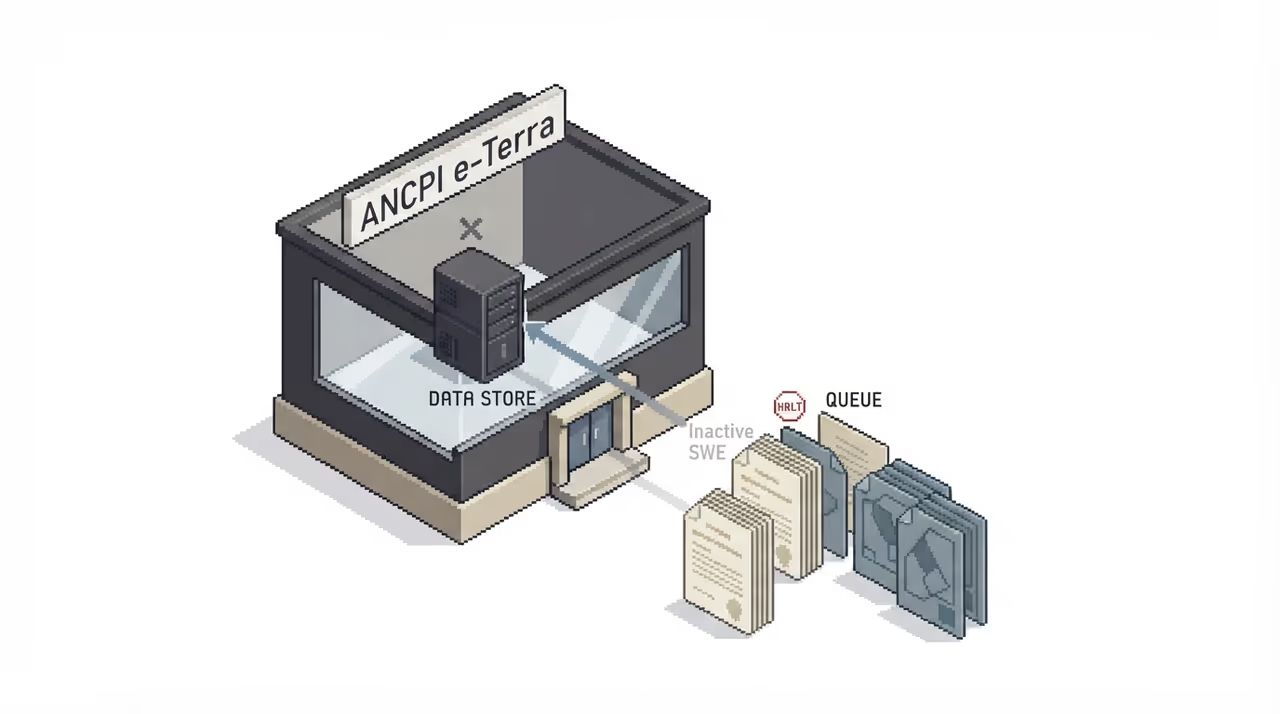
On Tuesday, July 14, 2026, Romania's National Agency for Cadastre and Land Registration (ANCPI) went dark. The outage took down e-Terra, the single nationwide platform that records every property sale, mortgage, and land title in the country, along with the agency's email and the apps notaries and lawyers rely on.
There is no fallback. e-Terra is the only system for registering property transactions in Romania, so when it stopped, the country's real estate market froze with it. Deals that needed a title update simply could not close.
ANCPI first called it a "technical incident." Within about 48 hours the label had climbed to "the most extensive technical disruption in the institution's history." That escalation is the first clue this was not a bad server day.
The break-in
No zero-day, just old bugs and old passwords
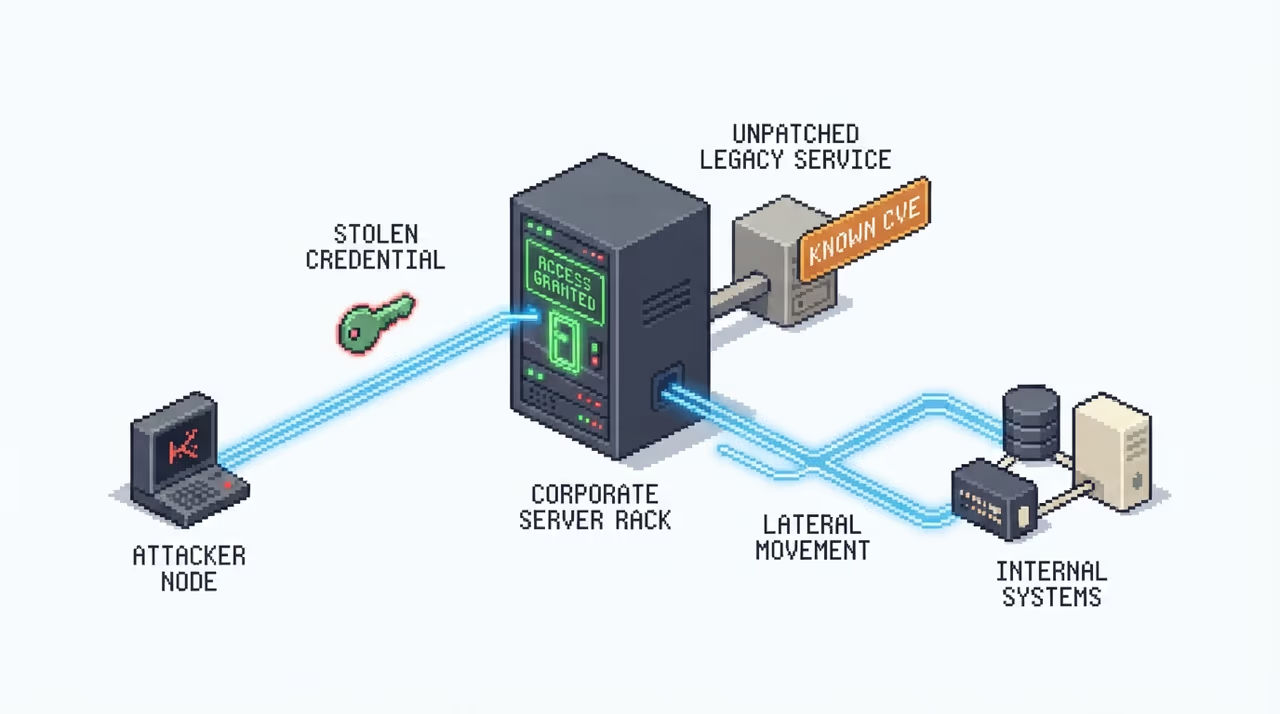
Dan Cimpean, director of Romania's cyber security agency DNSC, told outlet G4Media the break-in "wasn't a very complex attack." The attacker combined previously leaked credentials with known software vulnerabilities that authorities had recently warned organizations to patch.
Leaked credentialsKnown unpatched CVEInternal systems
That is the mundane, uncomfortable part. No exotic exploit chain, just valid logins that should have been rotated and patches that should have been applied. Once inside, the attacker moved laterally to map internal systems before making any demands.
The foothold may have predated the outage
Threat-intel firm Hudson Rock, cited by the aggregator dataaudit.net, claims it had flagged 89 compromised employee credentials and 4,500+ ANCPI user accounts already circulating on criminal markets via infostealer malware before July 14. This is a secondary claim and not independently confirmed, but if accurate it means the raw materials for the break-in were on sale well ahead of time.
The actor
ByteToBreach, an access broker for hire
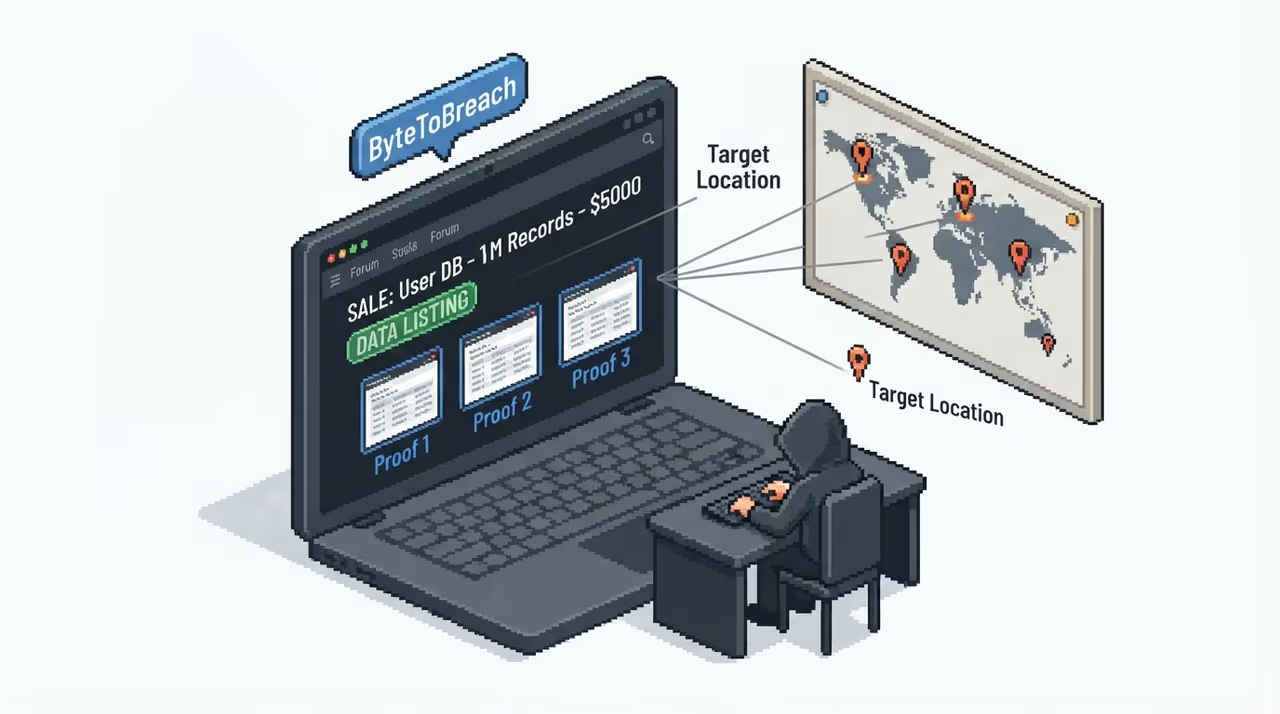
The attacker goes by ByteToBreach. Intelligence firm KELA Cyber assesses the actor as financially motivated, active since at least mid-2025, with a track record of hitting banking, telecom, and government targets across several countries. DNSC's Cimpean pegged them as an initial access broker, not a state-backed group.
This was not a one-off. ByteToBreach reportedly hit Latvia State Forests the month before and Sweden's e-government portal earlier in the year. Romania fit an existing pattern of serial government-sector breaches.
Romania joins Poland, Slovakia, Greece, Morocco, Russia, and Ukraine as countries whose land registries were hacked in the past three years.
After the ANCPI hack, KELA publicly named the person behind the alias: Zakaria Mahdjoub, reportedly based in Oran, Algeria. A person claiming to be the hacker even gave Euronews Romania a Signal interview, apologizing to Romanians, though Recorded Future News could not verify the identity.
The damage
Extortion first, then the wipe
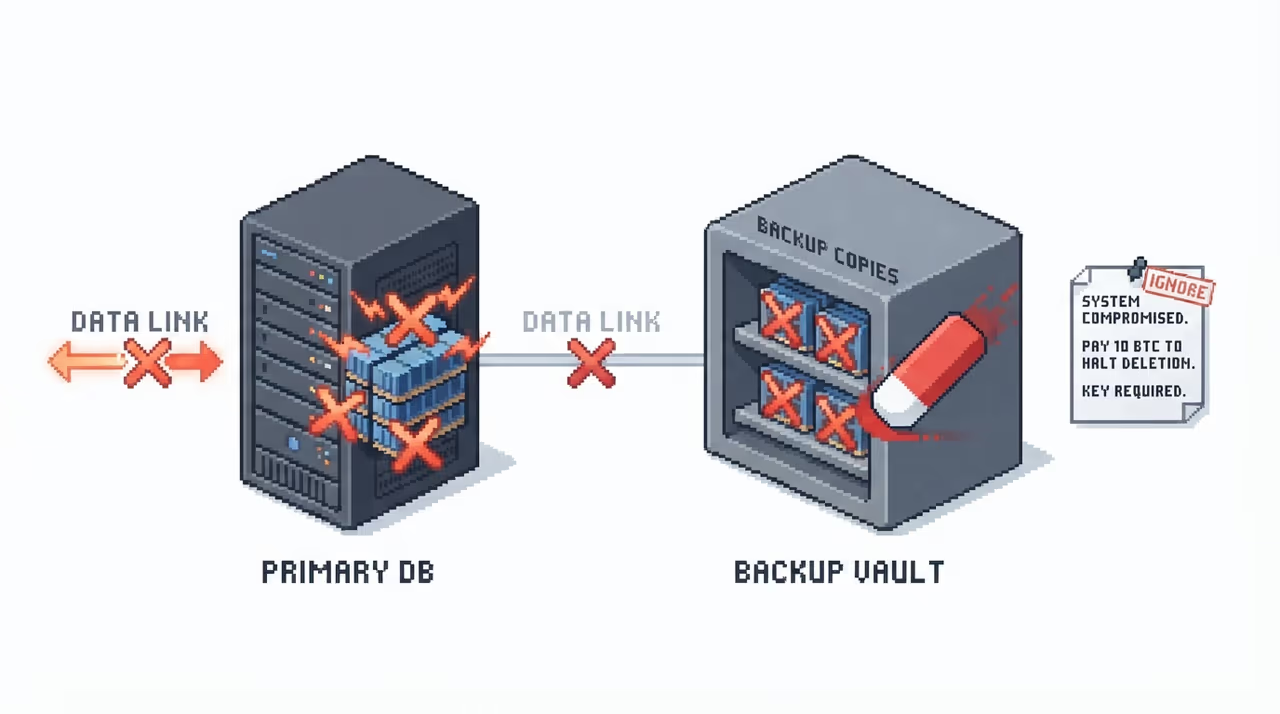
On July 15, ByteToBreach advertised ANCPI data on the DarkForums marketplace: citizen data, internal databases, and a copy of the GitLab servers holding source code for e-Terra, RENNS, and other systems. The post claimed a "little ransomware program" had been deployed.
According to Catalin Cimpanu's Risky Bulletin, sourced to unnamed insiders, the extortion attempt failed, and the attacker responded by wiping both the live database and its backups. Officials then posted about rebuilding the agency's entire network from scratch, which suggests they leaned on an offline backup copy to recover at all.
- Access via leaked creds + known CVE
- Lateral movement, data mapped
- Extortion demand
- Demand refused
- Live data + backups wiped
The lesson buried in that sequence: a wiper only wins if it can reach everything. An offline, air-gapped backup is the difference between a week-long outage and a permanent loss of a nation's property records.
Two stories
"Wiped" versus "not compromised"
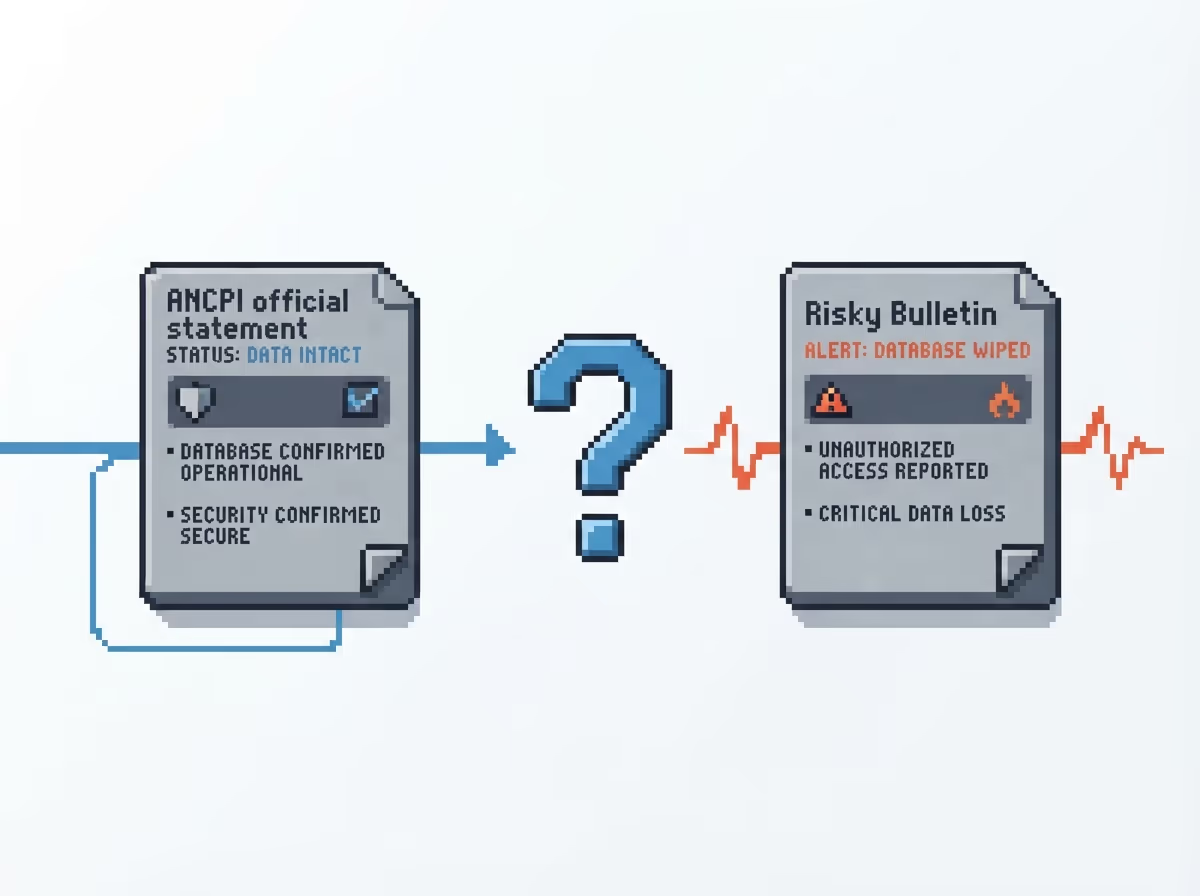
Here the accounts split, and it matters. ANCPI's own statements insist the core technical and legal databases (property boundaries, maps, ownership, mortgages) were not compromised, and that investigators found no evidence citizen data or land certificates were stolen.
ANCPI official line
core data intact, not compromised
Risky Bulletin sources
database and backups wiped
The "wipe" framing comes specifically from Risky Business's unnamed sources, not from ANCPI. A separate ransomware-encryption claim, based on Google-indexed .encrypted files, appears in only one low-authority blog and is not corroborated elsewhere. Treat both as reported, not confirmed.
By July 20, with the outage running nearly a week, ANCPI said it was migrating applications to the Romanian government cloud, aiming to finish mid-week and then verify integrity before a gradual restore. Cimpean noted attackers did exfiltrate a "limited amount" of data, including user credentials and application source code.
Why it lands
A national single point of failure, exposed
Why it matters
A single financially motivated actor, using leaked passwords and patches that were already public, froze an entire country's property market for a week. The attack shows how much national infrastructure rides on one system with no live alternative, and how thin the margin is between recovery and catastrophe when it comes down to whether an offline backup survived. The recovery, if the wipe reporting holds, hinged on exactly that.
The short version
- ByteToBreach got into ANCPI with **leaked credentials plus known, recently-patched vulnerabilities**, not a sophisticated exploit.
- After extortion failed, Risky Bulletin's sources say the attacker **wiped the live land registry and its backups**, forcing a network rebuild.
- ANCPI's official line contradicts this, insisting core data was **not compromised**, a tension the reporting has not resolved.
- e-Terra is Romania's **only** land registry system, so one outage froze the entire real estate market for roughly a week.
- Recovery appears to have depended on an **offline backup**, the one copy a wiper could not reach.
Sources
- 1.ANCPI Ransomware Attack: Romania’s Land Registry Down
- 2.The National Agency for Cadastre and Land Registration ...
- 3.Abbreviations ANCPI: Agentia Nationala de Cadastru si ...
- 4.ANCPI catalog open data in a single API request
- 5.ANCPI - ROeID - ROEID
- 6.Help Net Security: Romania's land registry hit by cyber attack, data allegedly for sale
- 7.The Record: Romania races to restore land registry after cyberattack disrupts property market
- 8.Risky Bulletin: Hacker wipes Romania's entire land registry database (Catalin Cimpanu)
- 9.Romanian Government Cadastre (ANCPI) cyber attack / ransomware
- 10.Slashdot - A hacker reportedly wiped Romania's entire land...
- 11.ANCPI - Startseite
- 12.ANCPI Definition
- 13.The National Agency for Cadastre and Land Registration ...
- 14.ANCPI
- 15.ANCPI - Agentia Nationala de Cadastru si Publicitate Imobiliara
- 16.Romanian Land Registry Hit by Cyber Attack and Ransomware Claims
- 17.Cyber Attack on Romania Land Registry: Exposed Data for Sale
- 18.Romania Land Registry Cyberattack Spurs ByteToBreach ...
- 19.KELA Cyber: Unmasking ByteToBreach
- 20.Dark Web Informer: Romanian Land Registry Agency ANCPI Allegedly Breached